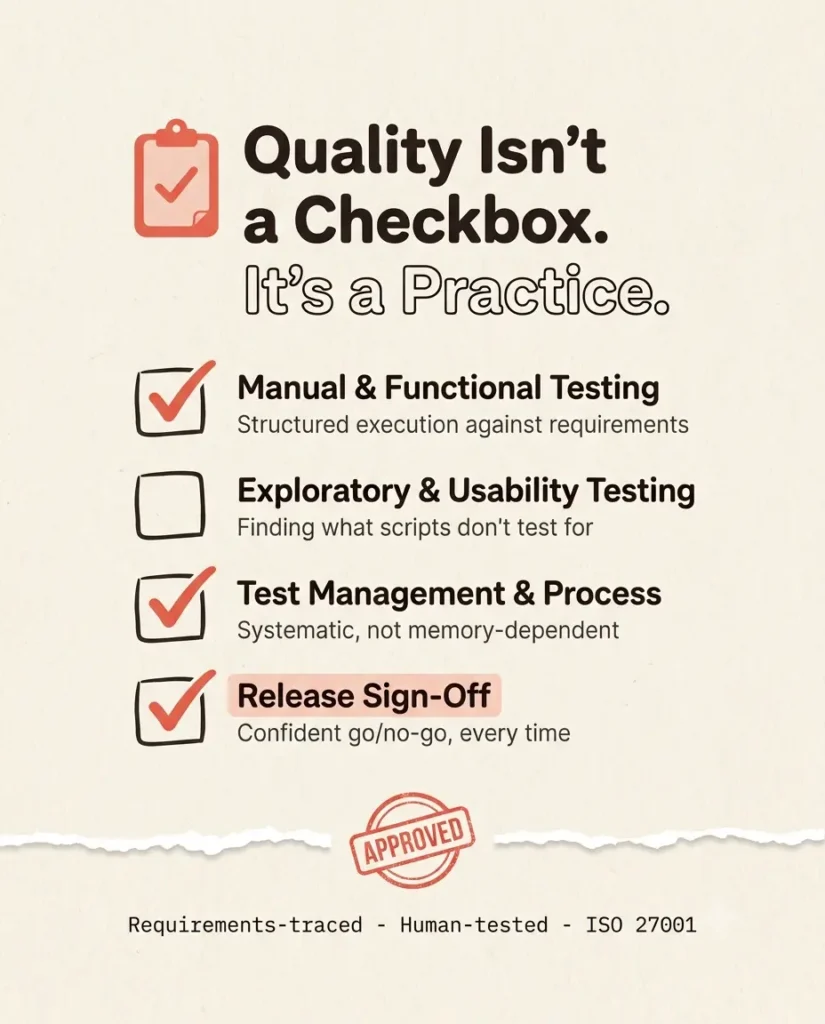
Quality isn't a
checkbox It's a practice.
We provide full QA coverage — manual testing, exploratory testing, test management and release sign-off — alongside automation where it makes sense. Senior QA engineers, fixed scope, a release process where “did we test this?” always has a confident answer.
180+ teams shipping with our engineers · ISO 27001-secure · NDA on request
— What we build
Four ways we bring
QA into your release process.
From a first manual test pass to a full QA practice with release sign-off, we build the coverage that matches what your automated tests can’t catch alone.
Manual & functional testing
Structured test case execution against requirements, catching what a script wasn’t written to check for.
Test case design
Functional testing
Requirements traceability
Exploratory & usability testing
Skilled testers actively probing the product the way real users would — finding the bugs nobody thought to write a test for.
Exploratory testing
Usability testing
Real-user simulation
Test management & QA process
Test case libraries, defect tracking and QA process design so quality is systematic, not dependent on one person’s memory.
Test case management
Defect tracking
QA process design
Release testing & sign-off
A structured go/no-go process before every release, so “is this ready to ship” has a confident, accountable answer.
Release readiness
Regression testing
Go/no-go sign-off
- Featured · The bugs automation doesn't catch
Automated tests check what you thought to test for. QA finds what you didn't.
Most “how did that bug get through” moments happen in the gap automation can’t cover — a confusing user flow, an edge case nobody scripted, a usability problem that’s technically “working as coded” but wrong in practice. Before we add process or automation, we find out where your current QA gap actually is — often it’s not more automated tests, it’s structured manual and exploratory testing that catches what scripts can’t.
Human judgment
Requirements-traced
Structured exploratory testing
Confident sign-off
1
AUDIT
Assess current QA coverage & gaps
2
DESIGN
Build test cases & exploratory testing charters
3
EXECUTE
Manual, exploratory and functional testing
Outcome
We start with a QA coverage audit — so testing effort goes where automation and existing process leave real gaps.
Services · Generative AI
Testing that ships you faster.
We design, build and run software testing — automated, performance, security, API, AI and continuous — wired into your pipeline so releasing gets faster, not scarier. Testing from engineers who build software, so we fix what we find. Senior teams, sprint-based delivery, measurable outcomes.
ISO 9001
Audited on quality
320+
Tests Automated
<2wk
Brief to first standup
96%
Client Repetition Ratio

Everything under One QA practice.
Each service is a fixed-scope engagement with a named senior lead and outcome targets agreed on Day 0. Start with the one where you break, or let us sequence them into a plan.
Automated Testing & QA Frameworks
Maintainable automation — unit, UI and regression — that catches bugs on every commit, not the night before release.
AI Model Testing & Validation
Ground-truth evals, red-teaming and drift monitoring for non-deterministic AI. You can’t unit-test a language model — so we test it like one.
Performance & Load Testing
Prove your system holds under real traffic, so the busiest day scales instead of crashing.
Security & Compliance Testing
Penetration testing plus SOC 2, ISO 27001, HIPAA and PCI — verified findings you can fix, not a PDF you file.
API & Integration Testing
Validate every API and integration — contracts, data and edge cases — so the services that must talk to each other, do.
Continuous Testing (CI/CD)
Testing wired into your pipeline with quality gates that block bad builds — so a green build means ship.
Not finding the service you need?
Tell us the outcome you’re after — we’ll scope a custom engagement.
Boring rigour behind bold ideas.
The reason our testing speeds teams up instead of slowing them down isn’t more tests — it’s the discipline around them. Four defaults on every engagement:
01
Test what matters
Risk-based, not 100%-coverage vanity. We test the paths that break and the ones the business can’t afford to lose.
02
Gates that block
A failing test stops the merge. Automation that can’t block a bad build is decoration, not a safety net.
03
No flaky tests
We treat flakiness as a bug, so red keeps meaning red — and your team keeps trusting the pipeline.
04
We fix, not just find
As engineers, findings come with fixes — a patch, a better test, a pipeline change — not a bug list handed over the wall.
THE STACK WE TEST ON
Automated for scale, human for judgment — on the CI/CD platform you already run.
Playwright
Cypress
Selenium
Appium
Postman
pytest
k6
JMeter
Burp Suite
OWASP ZAP
GitHub Actions
DeepEval
Industries
Quality assurance,
tuned for your industry.
Every industry has its own risk tolerance, compliance requirements and cost of a missed bug. We bring playbooks, not generic test checklists — and target QA effort at your organization’s real risk areas from day one.
Healthcare
QA that protects patient safety and compliance.
- Requirements-traced testing for clinical workflow accuracy
- Usability testing for patient-facing and clinician-facing tools
- Release sign-off meeting compliance documentation needs
Finance & Fintech
QA built for regulatory scrutiny and transaction accuracy.
- Functional testing for financial calculation accuracy
- Exploratory testing for edge cases in payment flows
- Release sign-off with full audit traceability
Retail & E-commerce
QA that protects the checkout experience.
- Usability testing for checkout and cart flows
- Cross-browser and cross-device functional testing
- Release sign-off timed around peak sales-event risk
Logistics
QA for systems where a missed bug means a missed shipment.
- Exploratory testing for routing and dispatch edge cases
- Functional testing for carrier and tracking integrations
- Release sign-off for always-on operational systems
Engagement models
Pick how you
want to Ship with us.
Three ways in — all senior QA engineers, all fixed against the release-confidence outcome we agree on before the first test case is written.
MVP
coverage audit
Best when you’re not sure where your current testing actually falls short.
- Fixed price, 1–2 weeks
- Coverage gap analysis across manual, exploratory and automated testing
- A prioritized QA roadmap
Most popular
Fixed-scope
Project-based build
Best for continuous testing coverage across your release cycle.
- Monthly retainer, scoped to your release cadence
- Manual, exploratory and functional testing included
- Release sign-off on every deploy
- Monthly QA reporting and process review
Embedded
Staff augmentation
Plug senior QA engineers into your team.
- 8+ yr average, hand-picked, never on a bench
- Manual, exploratory and test management skills
- Direct line to your engineering or product lead
FAQ
The QA & testing questions we get most
Still curious? Book a 30-min call with our QA delivery lead — no sales pitch, straight technical talk about where you break.
What testing do we actually need?
Rarely all of it. We start by finding where you break — slow under load, flaky in CI, exposed on security, or unreliable at the API layer — then point you to the two or three services that fix that. The six areas above are a menu, not a mandatory bundle.
Do you do both manual and automated testing?
Yes. We automate the repetitive regression so it runs on every commit, and keep experienced testers for exploratory testing and the judgment calls automation can’t make. Automating the boring part is what frees people for the part that needs a human.
Will adding testing slow our releases down?
The opposite, done right. We shift testing left into your pipeline and layer it for speed, so feedback comes back in minutes and a green build means ship. QA as a gate at the end slows you down; QA in the pipeline speeds you up.
Do you just find bugs, or fix them?
Both. Because we’re engineers who build software, findings come with fixes — a patch, a better test, a pipeline change — not just a list handed back over the wall.
Are you qualified — what are your credentials?
We’re ISO 9001:2015 (quality management) and ISO 27001:2018 (information security) certified, audited annually — so we’re independently held to the quality standard we test others against. Senior engineers only, NDA-friendly, DPA-ready.
ISO 27001-secure · Certified since 2020
Let's find out where quality is actually slipping.
Send your brief — a senior QA engineer (not a sales rep) replies within 24 hours with a read on your current QA coverage, and a fixed-scope plan for the gap.
- A 30-min scoping call with a senior QA engineer
- A QA coverage gap analysis
- A manual, exploratory and process design plan
- A release sign-off framework — yours to keep